

Best Control Mapping Software for Banks in MENA (2026)
Quick Answer: What Is the Best Control Mapping Software for Banks?
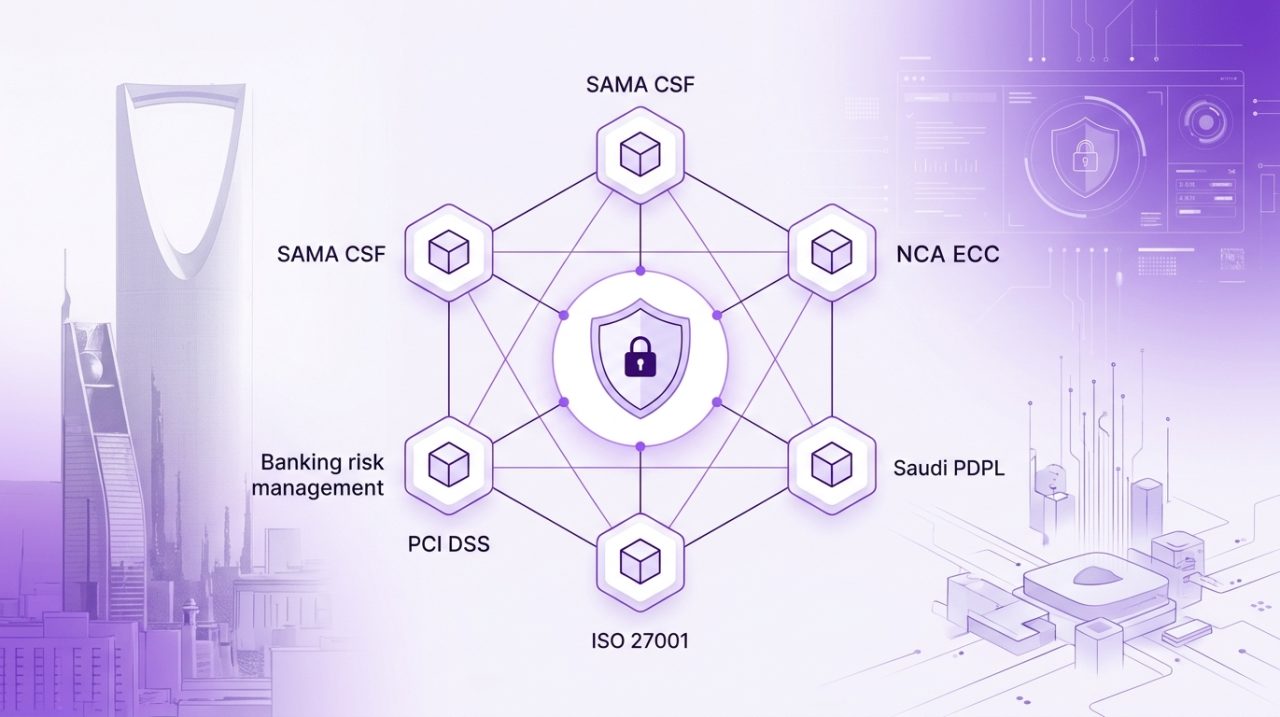
The best control mapping software for banks enables financial institutions to maintain one internal control library and map individual controls across multiple regulatory frameworks, including SAMA CSF, NCA ECC-2:2024, PDPL, ISO 27001 and PCI DSS.
Instead of implementing and documenting the same security control separately for every framework, banks can use cross-framework mapping to connect one internal control to multiple regulatory requirements and reuse supporting evidence.
For Saudi and GCC banks seeking regional regulatory coverage and pre-mapped frameworks, Sahl is our top recommendation. Larger financial institutions with dedicated GRC engineering teams may also consider Archer and ServiceNow GRC for their configurable enterprise capabilities.
The right choice ultimately depends on regulatory coverage, mapping accuracy, maturity tracking, evidence management, deployment requirements and implementation complexity.
What Is Control Mapping in GRC?
Control mapping is the process of linking an organisation’s internal controls to the external regulatory and compliance requirements they satisfy.
For example, consider a bank’s internal control:
Multi-factor authentication (MFA) for privileged access.
This control may support relevant requirements across several frameworks, including:
- NCA Essential Cybersecurity Controls (ECC).
- SAMA Cyber Security Framework (CSF).
- ISO 27001.
- PCI DSS.
Rather than creating separate controls and collecting duplicate evidence for each framework, control mapping software connects these requirements to a shared internal control.
Effective control mapping software helps organisations:
- Maintain a centralised control library.
- Map one control to multiple frameworks.
- Identify compliance gaps across frameworks.
- Reuse evidence across applicable requirements.
- Track control ownership and implementation status.
- Maintain mapping history as regulatory requirements change.
The result is a more consistent approach to compliance management and audit preparation.
Why Do Banks in MENA Need Cross-Framework Control Mapping?
Financial institutions across Saudi Arabia and the wider MENA region operate in increasingly complex regulatory environments.
A Saudi bank, for example, may need to manage several regulatory and industry requirements simultaneously.
1. SAMA Cyber Security Framework (CSF)
SAMA CSF establishes cybersecurity requirements for regulated financial institutions. Its maturity-based approach makes it important to monitor control implementation and maturity across relevant domains.
2. NCA Essential Cybersecurity Controls (ECC-2:2024)
NCA ECC-2:2024 establishes cybersecurity requirements across four main domains. Organisations within its scope must assess and demonstrate compliance with applicable controls.
3. Saudi Personal Data Protection Law (PDPL)
PDPL introduces requirements around personal data processing, consent, data subject rights, security and breach notification. Banks need appropriate privacy controls and supporting documentation to demonstrate compliance.
4. ISO 27001 and PCI DSS
International standards and industry requirements add further obligations around information security management and payment card data protection.
5. Additional regional requirements
Financial groups operating across multiple MENA countries may also need to address different local regulatory expectations, making centralised compliance management particularly valuable.
Without cross-framework mapping, compliance teams often maintain separate spreadsheets, duplicate evidence collection and repeat control assessments for different audits.
A centralised mapping approach helps reduce this duplication while providing a clearer view of the organisation’s overall compliance posture.
How We Evaluated the Best Control Mapping Software
We compared the platforms using criteria relevant to banks, fintechs and other regulated financial institutions in Saudi Arabia and MENA.
| Evaluation criterion | What banks should look for |
|---|---|
| Saudi regulatory coverage | SAMA CSF, NCA ECC-2:2024 and PDPL content |
| Cross-framework mapping | Many-to-many control mapping and version history |
| Maturity tracking | Domain-level maturity assessment and target levels |
| Evidence reuse | One evidence item linked to multiple applicable requirements |
| Audit readiness | Evidence history, review records and exportable audit reports |
| Third-party risk | Vendor assessments connected to relevant controls |
| Deployment | Cloud, private cloud and on-premises options where available |
| Arabic support | Arabic interfaces, documentation and regional support |
| Implementation | Time required to establish useful control mappings |
We distinguish between publicly described capabilities and features that should be confirmed directly with vendors. Actual implementation and framework coverage can vary by product edition and deployment.
The 6 Best Control Mapping Software Platforms for MENA Banks
1. Sahl – Best Overall for Saudi and GCC Banks
Sahl is an AI-powered GRC platform designed for organisations operating in Saudi Arabia and the wider MENA region.
Its regional regulatory focus makes it particularly relevant to banks and fintechs looking to manage multiple compliance frameworks through a centralised control environment.
Key capabilities include:
- Pre-mapped SAMA CSF, NCA ECC and PDPL frameworks.
- Cross-framework control mapping.
- ISO 27001, SOC 2 and PCI DSS coverage.
- Evidence collection and reuse across applicable requirements.
- Compliance dashboards and control status monitoring.
- AI DPO assistant for privacy-related support.
- Built-in DAST scanning.
- Arabic language support.
By connecting related requirements across frameworks, Sahl helps compliance teams avoid maintaining entirely separate control libraries for each regulatory obligation.
Its regional focus is particularly useful for organisations that need visibility into Saudi regulatory requirements alongside international standards.
Best for: Saudi and GCC banks, fintechs and insurers seeking regional regulatory coverage and centralised compliance management.
Consider: Banks looking for a broader enterprise-wide strategy, operational risk and crisis management suite should also evaluate larger configurable GRC platforms.
Website: https://getsahl.io/
2. CyberArrow – Best for Regional GRC Automation
CyberArrow is a regional GRC automation platform offering capabilities across cybersecurity, risk and compliance management.
Its framework coverage includes NCA ECC, SAMA CSF, ISO 27001, SOC 2 and PDPL, making it relevant to organisations managing multiple regulatory obligations.
Key considerations:
- Regional regulatory framework coverage.
- GRC and compliance automation.
- Risk and compliance management capabilities.
- Multi-framework requirements.
Best for: Regional organisations looking for a GRC platform with MENA-focused regulatory coverage.
Confirm with vendor: Depth of SAMA maturity tracking, cross-framework evidence reuse, built-in scanning capabilities and pricing structure.
Website: https://cyberarrow.io/
3. 6clicks – Best for Multi-Jurisdiction Compliance
6clicks is an AI-enabled GRC platform designed to support risk and compliance management across multiple frameworks and jurisdictions.
Its framework library and configurable assessment capabilities make it relevant to organisations with complex compliance requirements across different markets.
Key considerations:
- Extensive framework library.
- AI-assisted GRC capabilities.
- Risk and compliance workflows.
- Multi-framework assessment management.
- Sovereign infrastructure options.
Best for: Financial groups operating across multiple jurisdictions that need flexibility in managing different regulatory frameworks.
Confirm with vendor: Availability and maintenance of Saudi-specific framework mappings, Arabic support and the depth of native SAMA CSF and NCA ECC coverage.
Website: https://www.6clicks.com/
4. Archer – Best for Large Banks With Dedicated GRC Teams
Archer is an integrated risk management platform offering configurable workflows for enterprise risk, compliance, audit and policy management.
Its flexibility makes it suitable for large financial institutions with established governance structures and dedicated teams to manage complex GRC implementations.
Key considerations:
- Enterprise risk management.
- Configurable compliance workflows.
- Audit and policy management.
- Risk assessment and reporting.
- Customisable control environments.
Best for: Large banks with dedicated GRC administrators and technical resources to configure and maintain their compliance environments.
Confirm with vendor: Whether SAMA CSF, NCA ECC-2:2024 and PDPL are available as maintained, ready-to-use content or require additional configuration.
Website: https://www.archerirm.com/
5. ServiceNow GRC – Best for ServiceNow-Centric Financial Institutions
ServiceNow Governance, Risk and Compliance provides risk and compliance management capabilities within the wider ServiceNow platform.
Financial institutions already using ServiceNow for IT service management and enterprise workflows may find its integration capabilities valuable.
Key considerations:
- Integrated risk and compliance workflows.
- Policy and compliance management.
- Risk assessment and monitoring.
- Enterprise workflow automation.
- Integration with the broader ServiceNow ecosystem.
Best for: Large financial institutions already standardised on ServiceNow that want to extend existing workflows into risk and compliance management.
Confirm with vendor: How Saudi regulatory frameworks are delivered, whether control mappings are maintained and what additional implementation work is required.
Website: https://www.servicenow.com/
6. Ahkam GRC (RMG) – Best for a Local Software and Services Partner
Ahkam GRC, offered by Renad Al Majd Group (RMG), is a Saudi-focused GRC solution supporting organisations with governance, risk and compliance management.
Its positioning is relevant to organisations looking for local expertise alongside software-based compliance management.
Key considerations:
- Governance and compliance management.
- Policy lifecycle automation.
- NCA, SAMA and ISO 27001-related compliance support.
- Local implementation and services capabilities.
Best for: Saudi organisations that prefer working with a local technology and services partner for GRC implementation.
Confirm with vendor: The extent of native cross-framework mapping, evidence reuse, maturity tracking and available deployment models.
Website: https://rmg-sa.com/
Side-by-Side Comparison: Control Mapping Software for Banks
| Platform | Saudi framework coverage | Cross-framework evidence reuse | Best fit |
|---|---|---|---|
| Sahl | Pre-mapped regional frameworks | Supported | Saudi and GCC banks and fintechs |
| CyberArrow | Regional framework coverage | Confirm | Regional organisations |
| 6clicks | Saudi content availability | Confirm | Multi-country groups |
| Archer | Configuration-dependent | Confirm | Large enterprise banks |
| ServiceNow GRC | Configuration-dependent | Confirm | ServiceNow-centric institutions |
| Ahkam GRC | NCA, SAMA and ISO 27001 support | Confirm | Saudi organisations seeking local services |
Comparison note: This table reflects publicly described positioning and Sahl’s stated product capabilities. It is not a hands-on independent product test. Confirm framework versions, mapping depth, evidence reuse and implementation requirements with each vendor.
How to Choose the Right Control Mapping Software for Your Bank
The right platform depends on your institution’s regulatory scope, existing technology infrastructure and compliance maturity.
Here are four practical selection scenarios.
1. You are a Saudi bank or fintech looking for faster regulatory mapping.
Prioritise platforms with pre-mapped SAMA CSF, NCA ECC-2:2024 and PDPL content. Shortlist Sahl and CyberArrow and evaluate the accuracy and depth of their mappings.
2. You operate across multiple MENA countries.
Look for a platform that supports multiple jurisdictions and allows your team to maintain a centralised control library. Include 6clicks in your evaluation.
3. You are a large bank with an established technology team.
Consider Archer and ServiceNow GRC if you need extensive workflow configuration and integration with existing enterprise systems.
4. You need a local implementation and services partner.
Include Ahkam GRC in your shortlist and evaluate its software capabilities alongside its implementation and support services.
Run a Proof of Concept Before Making a Decision
Before selecting a platform, ask each shortlisted vendor to demonstrate the same practical scenario.
Give each vendor ten internal controls and ask them to:
- Map the controls to SAMA CSF, NCA ECC-2:2024 and PDPL.
- Identify overlapping requirements across the frameworks.
- Attach one evidence item to a control and demonstrate how it is reused.
- Show compliance gaps for each framework.
- Demonstrate SAMA maturity tracking.
- Export an audit-ready evidence report.
- Show how framework updates affect existing mappings.
Compare the number of manual steps, the accuracy of the mappings and the time required to complete the exercise.
A platform that looks impressive in a presentation should also demonstrate practical value using your organisation’s actual controls.
Frequently Asked Questions
The best solution should support SAMA CSF, NCA ECC-2:2024 and PDPL, alongside many-to-many control mapping, evidence reuse and maturity tracking. Sahl is designed around these regional compliance requirements.
Yes. The frameworks contain overlapping cybersecurity requirements in areas such as access control, incident management, logging and third-party risk management. However, individual requirements are not necessarily identical. Organisations should validate each mapping against the relevant framework versions and applicability criteria.
A compliance checklist tracks requirements separately for each framework. Control mapping connects one internal control to multiple applicable requirements, allowing organisations to reuse relevant evidence and manage overlapping obligations more efficiently.
Implementation time depends on the number of frameworks, existing control maturity, organisational complexity and mapping requirements. Platforms with pre-mapped framework content can accelerate initial setup, while highly customised implementations may require additional weeks or months.
Yes. A GRC platform can support all three frameworks through maintained regulatory content and cross-framework control mapping. However, banks should verify framework versions, mapping accuracy, applicable requirements and update processes before implementation.
Evidence reuse reduces repetitive documentation work. A single piece of evidence, such as an access review report, may support several applicable requirements across different frameworks. The evidence must still meet the specific scope and validation requirements of each mapped control.
Simplify Multi-Framework Compliance With Sahl
Managing SAMA CSF, NCA ECC-2:2024, PDPL and international standards does not have to mean maintaining separate control libraries and repeating the same evidence collection.
Sahl brings regional regulatory frameworks, cross-framework control mapping and compliance management into one AI-powered GRC platform.
For Saudi and GCC financial institutions looking to simplify compliance operations and improve audit readiness, explore how Sahl can support your GRC programme.

