

GRC Framework Saudi Arabia: NCA ECC, SAMA CSF & PDPL
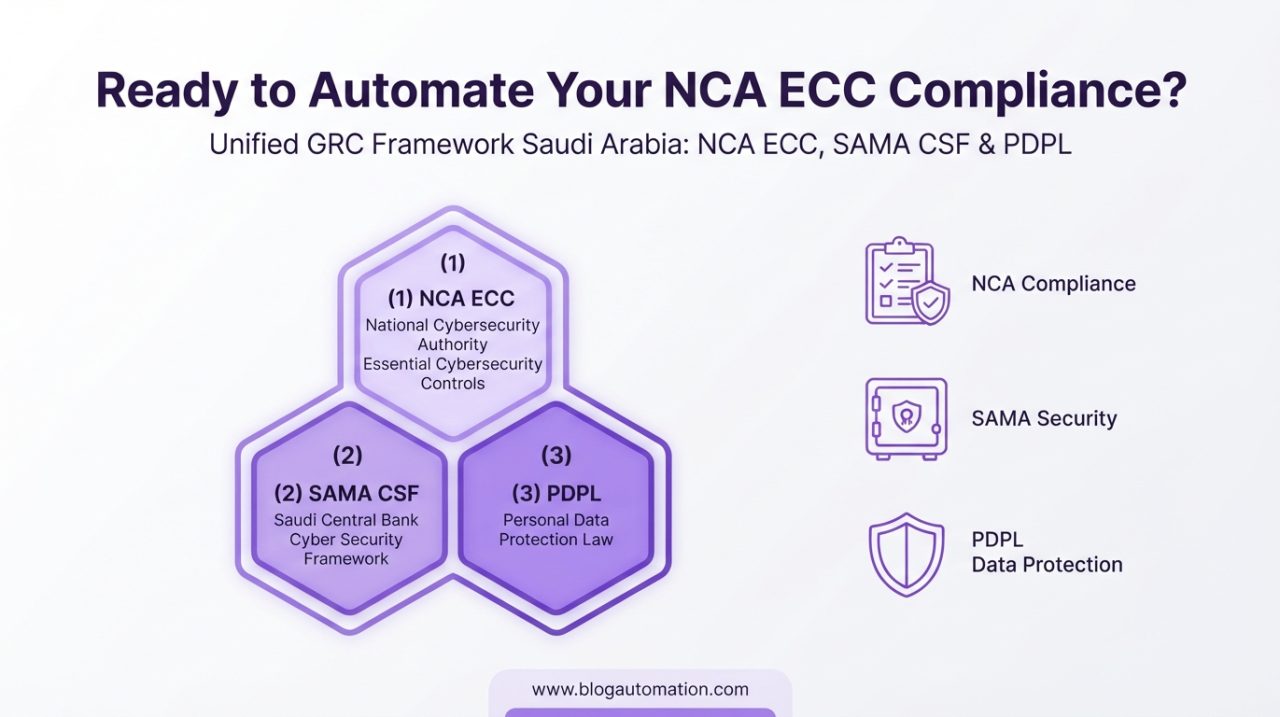
Large Saudi enterprises rarely face just one regulatory framework. A bank might need SAMA CSF for cybersecurity, KSA PDPL for personal data, and NCA ECC if it’s classified as having national importance — often all at once, often assessed by different internal teams working in isolation.
The result, without a unified approach, is duplicate work: three separate policy documents saying nearly the same thing, three separate evidence-collection processes for overlapping controls, and three audit cycles instead of one coordinated program.
This post explains how to cross-map these frameworks into a single control structure — and why that matters for CTOs and CISOs managing compliance at scale.
Where NCA ECC, SAMA CSF, and PDPL Overlap
While each framework has a distinct regulatory purpose, they share substantial structural overlap:
| Control Area | NCA ECC | SAMA CSF | KSA PDPL |
|---|---|---|---|
| Governance & accountability | Governance domain | Governance domain | DPO / accountability requirements |
| Risk management | Cybersecurity risk controls | Risk management domain | Risk-based processing safeguards |
| Access control & identity management | Explicit technical controls | Operations domain | Indirect (data protection by design) |
| Incident/breach response | Resilience domain | Operations domain | Breach notification requirement |
| Third-party & vendor risk | Third-party controls | Operations domain | Processor/vendor data handling |
| Data handling & residency | Infrastructure expectations | Indirect, financial data focus | Explicit transfer restrictions |
The pattern is clear: governance, risk management, incident response, and vendor oversight are near-universal requirements across all three frameworks, even though each uses different terminology and assessment methodology.
Why Managing These Separately Wastes Time
Duplicate Policy Documentation
Writing three separate information security policies one per framework when a single, well-structured policy could satisfy overlapping requirements across all three with minor framework-specific annexes.
Redundant Evidence Collection
Screenshotting the same access control configuration three times for three different auditors, instead of maintaining one piece of evidence mapped to all three frameworks simultaneously.
Disconnected Audit Calendars
Running NCA, SAMA, and internal PDPL reviews on separate, uncoordinated timelines multiplies the operational burden on the same underlying security and compliance teams.
Inconsistent Risk Views
When risk registers are maintained separately per framework, leadership never gets a single, accurate picture of the organization’s actual risk posture — just three partial, sometimes contradictory ones.
How to Build a Unified Control Framework
- Identify your applicable frameworks.
Confirm exactly which of NCA ECC, SAMA CSF, and PDPL apply to your organization based on sector, classification, and data handled. - Build a master control set.
Rather than starting from any single framework, define core control domains — governance, risk, access management, incident response, vendor risk, and data handling — that reflect the superset of what all applicable frameworks require. - Map each framework’s specific requirements to the master control set.
Document where each framework’s individual control maps to your unified structure — including where a framework has a requirement with no direct equivalent elsewhere. - Centralize evidence collection.
Collect evidence once per control, then tag it against every framework it satisfies, rather than collecting separately per framework. - Run a single coordinated risk register.
Maintain one risk view that feeds into all three frameworks’ risk management expectations, rather than three disconnected ones. - Schedule assessments with framework-specific deliverables, but shared preparation.
You’ll still need to produce NCA-specific, SAMA-specific, and PDPL-specific outputs — but the underlying preparation work should happen once.
Who Benefits Most From a Unified Approach
This approach delivers the most value for:
- Saudi banks and fintechs subject to SAMA CSF, PDPL, and often NCA ECC as government-adjacent entities
- Critical infrastructure operators managing NCA ECC alongside PDPL for customer data
- Large enterprises bidding on government contracts who need PDPL compliance for customer data and NCA ECC for the contract itself
- Any organization where the same security and compliance team is stretched across multiple frameworks
How Sahl Enables Cross-Framework Mapping
Sahl is built to manage this kind of multi-framework complexity:
- Native mapping across NCA ECC, SAMA CSF, and PDPL — showing where a single control satisfies multiple frameworks
- Centralized evidence collection — gather once, apply across every relevant framework automatically
- Unified risk register that feeds compliance reporting for all three frameworks from one source of truth
- Framework-specific report generation — so you still get the exact deliverables each regulator expects, without duplicating the underlying work
See Sahl’s unified compliance dashboard: https://getsahl.io/
Frequently Asked Questions
Yes. All three frameworks share substantial overlap in governance, risk management, incident response, and vendor oversight requirements, even though they use different terminology and assessment methods.
Often, yes. For example, an access control policy and its enforcement evidence can typically satisfy relevant requirements across NCA ECC, SAMA CSF, and PDPL simultaneously if mapped correctly, rather than requiring separate collection for each.
Banks, fintechs, and other SAMA-regulated entities that also handle personal data and may be classified as nationally significant are the most common example of organizations facing overlapping NCA ECC, SAMA CSF, and PDPL obligations.
It requires upfront structuring work, but tools that natively map multiple frameworks can significantly reduce the manual effort, making a unified approach realistic even for lean compliance teams.
Ready to Stop Managing Compliance in Silos?
Bring NCA ECC, SAMA CSF, and PDPL into one coordinated compliance program with Sahl.
See how Sahl unifies your compliance frameworks: https://getsahl.io/

