


Why Sprinto Falls Short for Saudi PDPL & NCA ECC | Sahl
The Short Answer
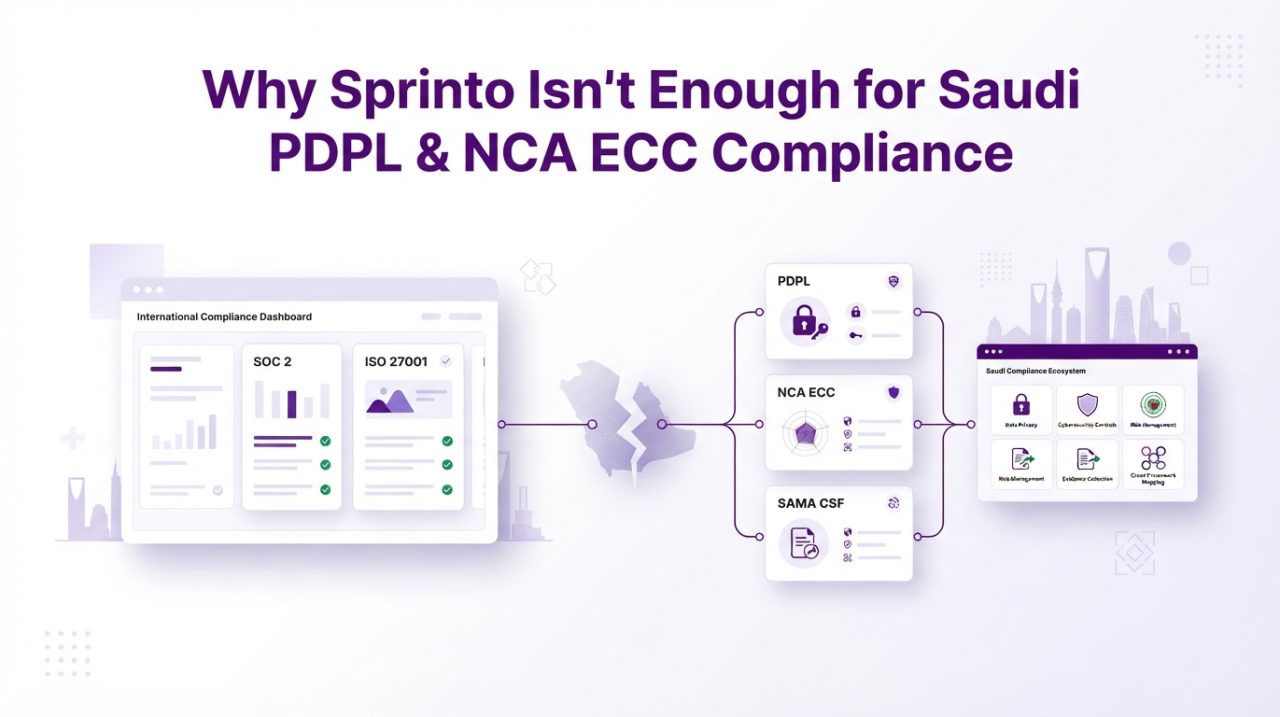
Sprinto is primarily designed around international compliance frameworks such as SOC 2 and ISO 27001. For organizations operating in Saudi Arabia, this can create a gap when compliance requirements extend to Saudi-specific frameworks such as PDPL and NCA ECC.
This does not mean Sprinto is a poor compliance platform. Its strengths are centered on automation and streamlined implementation for international frameworks.
The important question for Saudi organizations is whether their compliance platform can also address the specific regional requirements they need to manage.
This article explains where the Sprinto PDPL and NCA ECC coverage question becomes important and what Saudi organizations can consider instead.
Where the Gap Can Show Up
1. Saudi PDPL Requirements
Saudi PDPL introduces requirements related to personal data processing, data subject rights, privacy governance, data transfers, and personal data breach management.
Organizations using a platform primarily configured around international security frameworks may need additional processes to manage these Saudi-specific privacy obligations.
When PDPL requirements are not available as a native framework, teams may need to configure custom controls, maintain separate documentation, or use additional tools to track privacy compliance.
2. NCA ECC Requirements
The NCA Essential Cybersecurity Controls (NCA ECC) provide cybersecurity requirements specifically applicable within the Saudi regulatory environment.
While international frameworks such as SOC 2 and ISO 27001 contain controls that overlap with areas covered by NCA ECC, the frameworks are not interchangeable.
Saudi organizations may therefore need to maintain NCA ECC-specific control structures, evidence, and compliance workflows rather than relying solely on their existing international framework.
3. Regional Compliance Workflows
Compliance is not only about having individual controls. Organizations also need to maintain policies, evidence, ownership, assessments, remediation workflows, and audit documentation.
For Saudi organizations, managing regional requirements alongside global certifications can become more complex when the compliance platform does not provide native regional framework structures.
4. SAMA CSF for Regulated Organizations
Organizations operating in sectors regulated by the Saudi Central Bank (SAMA) may also need to address the SAMA Cyber Security Framework.
SAMA CSF has its own requirements and maturity-oriented approach. Financial institutions and other regulated entities should therefore evaluate whether their compliance platform supports the specific frameworks applicable to their regulatory environment.
5. Overlapping Controls Can Create More Manual Work
NCA ECC, SAMA CSF, PDPL, ISO 27001, and SOC 2 can contain overlapping areas such as access management, incident response, asset management, logging, and security governance.
Without appropriate cross-framework mapping, teams may end up managing similar requirements separately.
A platform that maps overlapping controls can help organizations collect evidence once and reuse it across applicable frameworks, reducing duplicate compliance work.
Why This Matters for Saudi Organizations
The main issue is not whether Sprinto can automate compliance workflows.
The question is whether an organization’s complete regulatory environment is represented inside its compliance platform.
A company may successfully manage SOC 2 or ISO 27001 while still needing separate processes for Saudi-specific requirements.
This becomes particularly important during:
- Regulatory assessments
- Customer due diligence
- Internal audits
- Third-party assessments
- Privacy reviews
- Security questionnaires
- Incident and breach response
Having a compliance platform does not automatically mean every applicable regulation is covered. Organizations should verify that the frameworks relevant to their jurisdiction and industry are actually represented in their compliance program.
What Saudi Organizations Can Do Instead
Organizations facing this challenge generally have two options.
Option 1: Use Multiple Platforms
A company can continue using an international compliance platform for frameworks such as SOC 2 and ISO 27001 while using another system, spreadsheet, or specialized process for Saudi-specific requirements.
This can work, but it may introduce:
- Duplicate evidence collection
- Separate control tracking
- Additional administrative work
- Multiple sources of compliance data
- More complicated reporting
Option 2: Use a Platform With Regional and Global Coverage
Another approach is to use a GRC platform that supports both international and Saudi-specific frameworks within the same environment.
Sahl is built around this approach.
Sahl provides native coverage for NCA ECC, SAMA CSF, and Saudi PDPL, alongside international frameworks such as SOC 2 and ISO 27001.
The platform also includes an AI DPO assistant designed to support PDPL-related workflows and cross-framework mapping to help organizations manage overlapping requirements more efficiently.
This allows organizations to bring regional and global compliance requirements into one GRC environment instead of maintaining separate systems for each framework.
How to Check If Your Organization Has a Compliance Gap
If you’re currently using Sprinto or another international compliance platform, ask these questions:
Does your platform include a native PDPL framework?
If PDPL has been manually recreated by your team, determine how much ongoing maintenance that requires and who is responsible for keeping the framework aligned with current requirements.
Can you manage NCA ECC requirements directly?
Check whether your platform provides a dedicated NCA ECC structure or whether your team is relying on custom controls and spreadsheets.
Can you reuse evidence across frameworks?
If the same access-control evidence has to be uploaded and managed separately for different frameworks, there may be an opportunity to reduce manual work through cross-framework mapping.
Can you produce regional compliance evidence quickly?
If a regulator, customer, or auditor requested Saudi-specific evidence, consider how quickly your team could locate the relevant controls, documentation, and evidence.
Are your global and regional frameworks managed in one place?
If SOC 2 and ISO 27001 are managed in one platform while PDPL and NCA ECC are tracked elsewhere, your organization may benefit from consolidating its compliance workflows.
Frequently Asked Questions
Organizations evaluating Sprinto for PDPL should verify the platform’s current framework catalog and capabilities directly. Sprinto is primarily positioned around international compliance frameworks such as SOC 2 and ISO 27001, so Saudi organizations should confirm whether their specific PDPL requirements are available natively or require additional configuration.
Saudi organizations should verify Sprinto’s current framework catalog for NCA ECC support. NCA ECC has Saudi-specific control requirements that should be assessed separately from international frameworks such as SOC 2 and ISO 27001.
Yes. Organizations can use separate systems for different compliance requirements. However, this can create additional evidence management, control tracking, and reporting work.A platform that supports both global and regional frameworks can help reduce this duplication.
Sahl is designed for organizations that need both regional and international compliance coverage. It supports NCA ECC, SAMA CSF, and Saudi PDPL alongside SOC 2 and ISO 27001, allowing organizations to manage these requirements within one GRC platform.
Native framework support can reduce the need to manually recreate controls, requirements, mappings, and evidence structures. It can also make ongoing compliance management more consistent and easier to maintain.
The Bottom Line
Sprinto can be a strong option for organizations focused on streamlined international compliance automation.
For Saudi organizations, however, the compliance conversation can extend beyond SOC 2 and ISO 27001.
PDPL, NCA ECC, and SAMA CSF introduce regional requirements that should be explicitly addressed within the organization’s compliance program.
If your current platform requires separate tools, spreadsheets, or manually configured frameworks to manage those requirements, it may be worth evaluating a GRC platform designed to bring regional and global compliance together.
Sahl combines Saudi-specific frameworks such as NCA ECC, SAMA CSF, and PDPL with global frameworks such as SOC 2 and ISO 27001.
Book a demo with Sahl and explore what unified Saudi and global compliance management can look like for your organization.

