

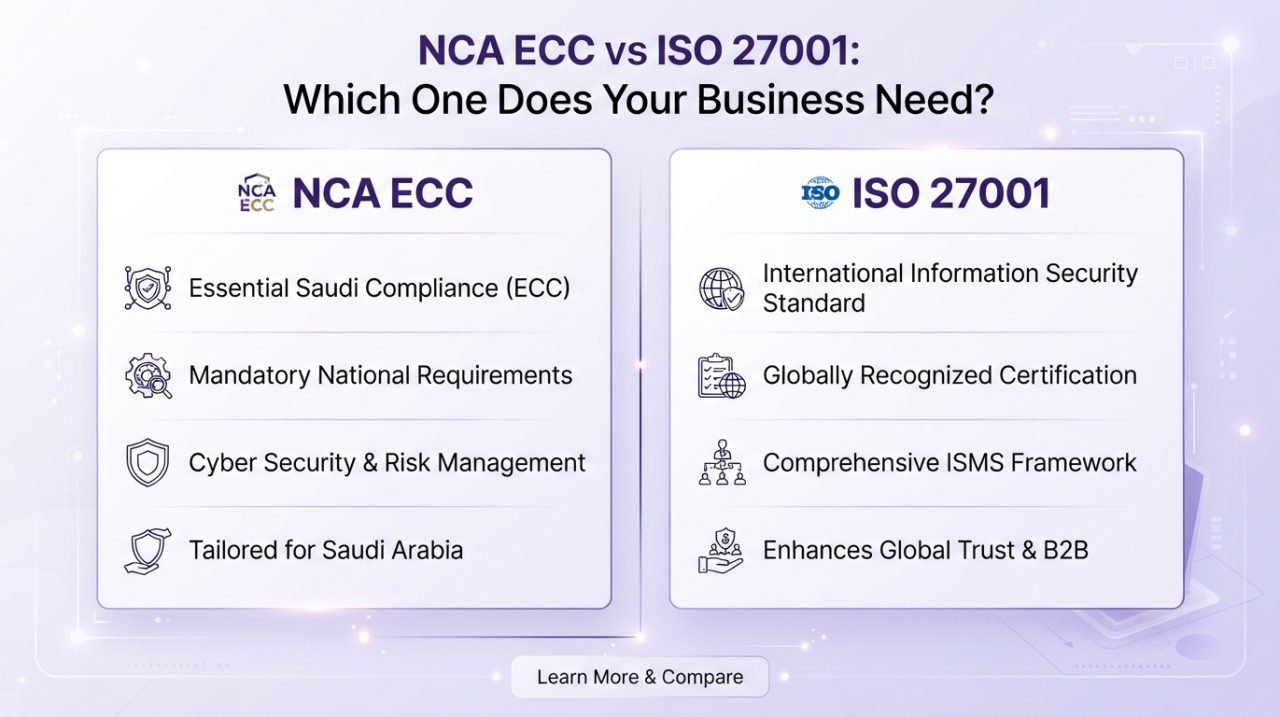
NCA ECC vs ISO 27001: Which One Does Your Business Need?
Executive Summary
NCA Essential Cybersecurity Controls (ECC) and ISO/IEC 27001 are two important cybersecurity and information security frameworks, but they serve different purposes.
The NCA ECC is a Saudi Arabia-specific cybersecurity control framework issued by the National Cybersecurity Authority (NCA). Its applicability depends on the entity and the NCA’s relevant regulatory requirements. ISO/IEC 27001, meanwhile, is an internationally recognized standard for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS).
For organizations operating in Saudi Arabia, the two frameworks should not necessarily be viewed as alternatives. Depending on regulatory obligations, customer requirements, and business objectives, an organization may benefit from aligning with both.
The key is to identify common controls, avoid duplicate work, and manage evidence through a unified compliance process.
Key Takeaways
- NCA ECC: A Saudi cybersecurity control framework designed to strengthen cybersecurity across applicable organizations and sectors in the Kingdom.
- ISO/IEC 27001: An internationally recognized standard for managing information security through a risk-based ISMS.
- Different purposes: NCA ECC addresses Saudi-specific cybersecurity requirements, while ISO 27001 provides a globally recognized management-system framework.
- Significant overlap: Many security domains and controls are conceptually aligned, although the exact mapping depends on the versions and scope being compared.
- Using both: Organizations subject to NCA requirements may also pursue ISO 27001 when international customers, partners, procurement requirements, or internal governance objectives call for it.
- Centralized compliance: A GRC platform such as Sahl can help organizations map controls, centralize evidence, monitor gaps, and reduce repetitive compliance work.
Navigating the Compliance Landscape in Saudi Arabia
For CISOs, compliance teams, and security leaders operating in Saudi Arabia, understanding NCA ECC vs ISO 27001 is increasingly important.
Saudi organizations may need to address multiple cybersecurity and information security requirements at the same time. A government entity, regulated organization, SaaS provider, or enterprise serving international customers may therefore have to manage both local regulatory expectations and internationally recognized security standards.
This creates an important question:
Do you need NCA ECC, ISO 27001, or both?
The answer depends on your organization’s regulatory obligations, industry, customers, contractual requirements, and security objectives.
Rather than treating each framework as a separate compliance project, organizations can take a unified approach by identifying common requirements and reusing controls and evidence wherever appropriate.
The Core Difference: Saudi Cybersecurity Requirements vs. International ISMS
The most important distinction between NCA ECC and ISO 27001 is their purpose and structure.
What is NCA ECC?
The National Cybersecurity Authority (NCA) Essential Cybersecurity Controls (ECC) provides a set of cybersecurity controls designed for the Saudi context.
The controls address areas such as:
- Cybersecurity governance
- Asset management
- Identity and access management
- Network security
- Vulnerability management
- Incident management
- Business continuity
- Third-party and cloud security
- Cybersecurity awareness
- Data and information protection
The framework is intended to establish a baseline of cybersecurity requirements for organizations within its applicable scope.
What is ISO 27001?
ISO/IEC 27001 is an international standard for an Information Security Management System (ISMS).
Rather than simply prescribing a fixed list of technical security measures, ISO 27001 requires organizations to establish a systematic, risk-based approach to information security.
An ISO 27001 program typically includes:
- Information security policies
- Risk assessment and risk treatment
- Defined security objectives
- Roles and responsibilities
- Security controls
- Monitoring and measurement
- Internal audits
- Management review
- Continual improvement
This makes ISO 27001 particularly useful for organizations that want to demonstrate a structured approach to information security to customers, partners, regulators, and other stakeholders.
NCA ECC vs ISO 27001: Comparison
| Feature | NCA ECC | ISO/IEC 27001 |
|---|---|---|
| Origin | Saudi National Cybersecurity Authority | International Organization for Standardization / IEC |
| Geographic focus | Saudi Arabia | International |
| Primary purpose | Establish cybersecurity controls applicable to organizations within its scope | Establish and continually improve an Information Security Management System |
| Approach | Control and requirement-oriented | Risk-based management-system approach |
| Applicability | Depends on the organization and applicable NCA requirements | Voluntary unless required by contract, regulation, procurement, or organizational policy |
| Certification | Compliance is determined according to applicable Saudi requirements and assessment arrangements | Organizations can pursue accredited ISO 27001 certification |
| Business value | Supports alignment with Saudi cybersecurity requirements | Demonstrates internationally recognized information security governance |
| Typical use | Saudi regulatory and cybersecurity compliance | Global customers, governance, risk management, and information security assurance |
How Much Do NCA ECC and ISO 27001 Overlap?
One of the biggest advantages of implementing both frameworks is that they address many similar security domains.
Common areas can include:
- Asset management
- Access control
- Information security governance
- Human resources security
- Incident management
- Business continuity
- Third-party security
- Security monitoring
- Risk management
- Information and data protection
However, organizations should be careful with blanket claims such as “NCA ECC and ISO 27001 have 60–70% control overlap.”
The actual percentage depends on the specific versions of the frameworks, the mapping methodology, and the organization’s implementation scope.
The more useful approach is to perform a formal crosswalk between the applicable NCA ECC requirements and ISO 27001 controls rather than relying on a single overlap percentage.
This is where a GRC platform can provide significant value.
Instead of maintaining separate spreadsheets for every framework, organizations can map common controls and connect the relevant policies, procedures, risks, and evidence to multiple requirements.
Do You Need Both NCA ECC and ISO 27001?
There is no universal requirement for every organization to implement both.
Your decision should be based on your organization’s regulatory and commercial requirements.
NCA ECC May Be the Priority When:
- Your organization falls within the scope of applicable NCA requirements.
- You operate in a Saudi government or regulated environment.
- Your customers or stakeholders require alignment with Saudi cybersecurity requirements.
- Your organization needs to demonstrate compliance with applicable Saudi cybersecurity controls.
ISO 27001 May Be Valuable When:
- You serve international customers.
- Enterprise customers request ISO 27001 certification.
- You participate in international procurement processes.
- Your organization needs a formal ISMS.
- You want a structured risk-management and continual-improvement framework.
- Security assurance is an important part of your sales process.
Both May Make Sense When:
An organization can have both local regulatory obligations and international commercial requirements.
For example, a Saudi-based SaaS company may need to address applicable Saudi cybersecurity requirements while also responding to enterprise customers that require ISO 27001 certification.
In that situation, maintaining two completely separate compliance programs can create unnecessary duplication.
A unified control environment can help the organization satisfy overlapping requirements while maintaining separate evidence and assessments where the frameworks differ.
How to Manage NCA ECC and ISO 27001 Efficiently
The biggest challenge with multiple compliance frameworks is not necessarily implementing individual controls.
It is managing the relationships between controls, risks, policies, owners, and evidence.
A typical organization may otherwise end up with:
- Duplicate policies
- Multiple evidence repositories
- Repeated evidence requests
- Separate compliance spreadsheets
- Manual control mapping
- Repetitive audit preparation
- Unclear control ownership
A centralized GRC approach can reduce this complexity.
For example, one access-control policy may support requirements across multiple frameworks. Instead of uploading and reviewing the same evidence repeatedly, the organization can associate that evidence with all relevant controls.
This creates a “build once, map many” approach to compliance.
How Sahl Can Help
Sahl helps organizations manage compliance requirements through a centralized GRC platform.
With cross-framework mapping, teams can connect common controls and evidence across frameworks such as NCA ECC and ISO 27001, rather than managing every framework independently.
Sahl can help teams:
- Map controls across multiple frameworks
- Centralize compliance evidence
- Assign control ownership
- Monitor compliance status
- Identify control gaps
- Track remediation activities
- Prepare audit documentation
- Reduce repetitive evidence collection
- Maintain a centralized view of compliance posture
Instead of asking your team to maintain separate compliance programs for every framework, Sahl can help create a connected compliance environment.
One control. Multiple requirements. One source of evidence.
Frequently Asked Questions
No. NCA ECC is a Saudi cybersecurity framework, while ISO 27001 is an international standard for managing information security.
It depends on your regulatory and business requirements. ISO 27001 may be needed for international customers, contracts, or certification requirements.
No. ISO 27001 certification does not automatically mean NCA ECC compliance. Organizations must address applicable NCA ECC requirements separately.
Start with the requirements that apply to your organization. If both apply, you can align their overlapping controls to reduce duplicate work.
Sahl centralizes controls, evidence, and compliance tracking, making it easier to identify gaps and prepare for audits.
Yes. Sahl helps organizations map controls and manage evidence across NCA ECC, ISO 27001, and other frameworks in one place.
NCA ECC vs ISO 27001: The Bottom Line
NCA ECC and ISO 27001 serve different purposes and should not necessarily be viewed as competing frameworks.
Saudi-specific cybersecurity requirements are addressed by NCA ECC, while ISO 27001 provides an internationally recognized approach to information security management.
For organizations operating in Saudi Arabia, the right strategy depends on regulatory scope, customer expectations, industry requirements, and business goals.
Where both frameworks apply, the most efficient approach is often to align overlapping controls rather than build two completely separate compliance programs.
With the right GRC platform, organizations can centralize evidence, map controls across frameworks, track gaps, and create a more efficient path to ongoing compliance.
Ready to simplify your compliance program?
Explore Sahl and see how multi-framework compliance can work for your organization →

