


Saudi Data Residency: PDPL & NCA Cloud Compliance
For organizations storing or processing personal or sensitive data connected to Saudi Arabia, one question often comes up early in the cloud-planning process: where, physically, is this data stored and processed?
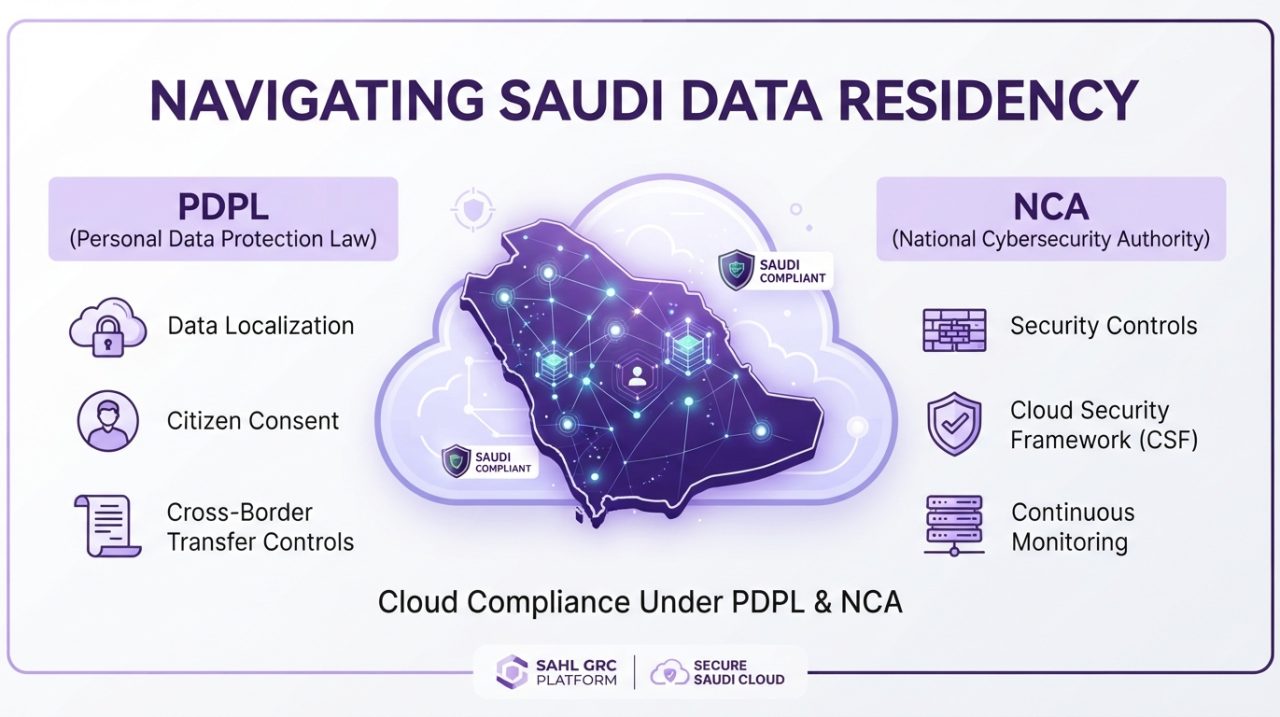
The answer matters because Saudi Arabia’s data protection and cybersecurity framework does not treat all data, organizations, or cloud workloads identically. The Personal Data Protection Law (PDPL) establishes requirements for transferring personal data outside the Kingdom, while the National Cybersecurity Authority (NCA) has issued cybersecurity controls that address cloud computing, data protection, and, for applicable entities and workloads, information hosting and storage inside Saudi Arabia.
For organizations designing a Saudi cloud strategy, the practical question is therefore not simply “Can our data leave Saudi Arabia?” It is:
What data are we handling, which requirements apply to our organization, where will the data be stored and processed, and what safeguards or controls are required?
This guide breaks down the key considerations.
What Is Data Residency, and Why Does It Matter in Saudi Arabia?
Data residency refers to the physical or jurisdictional location in which data is stored or processed.
In Saudi Arabia, residency considerations can arise from several overlapping requirements. The applicable obligations depend on factors such as the type of data, the organization’s regulatory status, the nature of the cloud service, and the cybersecurity controls applicable to the organization.
Three areas are particularly important:
- PDPL: governs the processing of personal data and establishes conditions for transferring or disclosing personal data outside the Kingdom.
- NCA controls: establish cybersecurity requirements for applicable entities, including requirements relating to cloud computing and data protection.
- Sector-specific requirements: regulated sectors such as financial services may have additional requirements that need to be assessed alongside the general Saudi framework.
The NCA’s current Cloud Cybersecurity Controls (CCC 2:2024) specifically address cloud service providers and cloud service tenants and were updated to reflect changes related to data localization requirements.
This means cloud architecture should be assessed against the specific regulatory scope of the organization and workload, rather than relying on a blanket assumption that every Saudi-related dataset must—or may—be hosted in exactly the same way.
Cross-Border Data Transfer Under the Saudi PDPL
The PDPL does not impose a blanket prohibition on transferring personal data outside Saudi Arabia.
Article 29 permits certain transfers or disclosures outside the Kingdom, subject to conditions including protection of national security and vital interests and requirements concerning the level of protection available for personal data outside the Kingdom.
The Regulation on Personal Data Transfer Outside the Kingdom provides additional requirements for such transfers. It allows a controller to transfer or disclose personal data to a party outside Saudi Arabia provided the transfer does not prejudice national security or the Kingdom’s vital interests and the applicable regulatory requirements are satisfied.
Depending on the circumstances, organizations may need to consider:
- Whether the destination provides an adequate level of protection
- Whether appropriate safeguards are required
- The purpose and legal basis for the transfer
- The geographic scope and nature of the processing
- Whether the transfer is limited to the minimum personal data necessary
- Potential risks to data subjects
- Measures used to prevent or mitigate those risks
The implementing framework also identifies circumstances involving continuous or large-scale transfers of sensitive data as requiring particular attention to transfer risk assessment.
Practical implication
Before choosing a cloud region outside Saudi Arabia, organizations should document why the transfer is allowed and which safeguards apply.
When regulations require data to stay in Saudi Arabia, an in-Kingdom deployment can simplify data residency.
NCA Cloud and Data Localization Requirements
The NCA framework adds another layer to cloud compliance.
The Essential Cybersecurity Controls (ECC 2:2024) include requirements relating to the use of hosting and cloud computing services. The controls state that, for applicable requirements, organizations should classify data before hosting it on cloud or hosting services and ensure that organization information hosting and storage is inside the Kingdom of Saudi Arabia.
The NCA’s Cloud Cybersecurity Controls (CCC 2:2024) extend the cybersecurity framework specifically to cloud service providers and cloud service tenants. The NCA states that the updated controls reflect changes related to data localization requirements.
The important takeaway is that NCA compliance should be assessed according to the organization’s applicable control scope, rather than treating “NCA” as a single universal cloud-hosting rule.
For organizations subject to the relevant NCA controls, cloud architecture should therefore address:
- Data classification before cloud deployment
- Physical hosting and storage location
- Cloud service provider responsibilities
- Cloud tenant responsibilities
- Security controls around the data lifecycle
- Data return and deletion considerations when a cloud service ends
- Third-party and cloud-service risks
The NCA’s Data Cybersecurity Controls also establish requirements intended to protect data throughout its lifecycle.
Regional Cloud Hosting vs. In-Kingdom Hosting
One of the easiest mistakes to make is treating “Middle East region” and “Saudi Arabia region” as interchangeable.
They are not necessarily the same thing.
A cloud provider may market a geographic region as Middle East, GCC, or another regional designation while the physical infrastructure serving that region is located outside Saudi Arabia.
For workloads subject to an in-Kingdom hosting or storage requirement, the relevant question is therefore:
Where is the actual data stored and processed?
When evaluating a cloud provider, verify:
| Factor | Why It Matters |
|---|---|
| Physical data-center location | Confirms whether data is actually stored inside Saudi Arabia |
| Data-processing locations | Storage residency alone may not describe every processing location |
| Backup and disaster-recovery locations | Copies of data may be stored separately from primary workloads |
| Contractual data-location commitments | Helps establish where the provider is permitted to store and process data |
| Subprocessor locations | Third-party services can introduce additional transfer considerations |
| Data deletion and exit procedures | Helps demonstrate what happens to data when the service ends |
| Compliance evidence | Supports audits and demonstrates the organization’s residency posture |
Cloud providers use regional marketing labels for convenience, but organizations should always verify them through contractual and technical checks.
Cloud Hosting Options for Saudi Organizations
Major international and Saudi cloud providers have expanded their infrastructure and cloud offerings in the Kingdom.
However, availability of a Saudi data center does not automatically mean every service offered by that provider is available in Saudi Arabia.
Organizations should verify the specific:
- Cloud region
- Service availability
- Storage location
- Backup location
- Disaster-recovery architecture
- Processing location
- Subprocessor arrangements
- Contractual residency commitments
This distinction is particularly important when evaluating a cloud platform for regulated or sensitive workloads.
Don’t Forget Your Compliance Tooling
Production systems are not the only systems that can contain sensitive organizational information.
Compliance platforms may store:
- Records of processing activities (RoPA)
- Data inventories
- Data-flow information
- Audit evidence
- Security documentation
- Breach records
- Vendor and processor information
- Information about internal systems and controls
That means organizations should evaluate the data residency and processing architecture of their compliance tooling, not just their production cloud environment.
A platform that helps manage Saudi compliance should itself be assessed for:
- Where customer data is hosted
- Where backups are stored
- Where processing occurs
- Whether subprocessors are involved
- Whether cross-border transfers can occur
- What contractual commitments govern data location
- How data is deleted or returned
For organizations with strict Saudi residency requirements, these questions should form part of the vendor due-diligence process.
How Sahl Supports Saudi Data Residency Compliance
Sahl is designed to help organizations manage the compliance information associated with Saudi data protection requirements.
Its capabilities include:
- Saudi-focused compliance infrastructure for compliance evidence and documentation
- Data mapping and cross-border transfer tracking
- Documentation support for reviewing and recording transfer safeguards
- Audit-ready compliance reporting
- Centralized records for data-processing and privacy activities
This helps organizations move beyond simply identifying where their production data is hosted and build a broader view of where personal-data-related information flows across their environment.
See how Sahl supports Saudi PDPL compliance →
A Practical Saudi Data Residency Checklist
Before approving a cloud architecture for a Saudi workload, ask:
1. What type of data are we processing?
Identify personal data, sensitive personal data, confidential business information, and other regulated categories.
2. Which regulations and controls apply?
Determine whether the organization falls within the scope of relevant NCA controls, PDPL requirements, sector-specific regulations, or contractual obligations.
3. Where Do You Store the Primary Data?
Confirm the physical location rather than relying on a generic geographic region.
4. Where is data processed?
Storage location and processing location may not always be identical.
5. Where are backups stored?
Disaster recovery and backup environments should be included in the residency assessment.
6. Are any subprocessors located outside Saudi Arabia?
Third-party services can create additional data-transfer considerations.
7. If personal data leaves Saudi Arabia, what legal requirements apply?
Document the purpose, legal basis, destination, safeguards, and risk assessment where required.
8. Does the contract guarantee the required data location?
Get residency commitments into the contractual documentation rather than relying solely on sales or marketing material.
9. What happens when the cloud contract ends?
Confirm how data is returned, deleted, archived, or otherwise handled.
10. Does our compliance software follow the same residency strategy?
Review the location of compliance evidence, RoPA records, audit trails, and other privacy documentation.
Frequently Asked Questions
No, not universally. However, the PDPL allows certain cross-border transfers when organizations meet applicable conditions and safeguards. The Transfer Regulation also sets additional requirements for these transfers.
Requirements depend on the organization and applicable NCA controls. The ECC and Cloud Cybersecurity Controls address cloud hosting, data storage, and localization requirements.
Regional hosting serves a broader geographic area, while in-Kingdom hosting means the infrastructure is physically located in Saudi Arabia. Therefore, organizations should verify the actual storage and processing locations instead of relying on regional cloud labels.
Yes. A complete residency assessment should cover the production environment, backups, disaster-recovery systems, replicas, and any other locations that store or process data.
The exact requirement depends on the data and applicable regulations. However, compliance platforms may store sensitive information, so organizations should include them in data-location and vendor-risk assessments.
Several international and Saudi cloud providers have developed or announced infrastructure and services in the Kingdom. However, cloud-region availability and individual service availability can change. Organizations should verify the current region, service, processing location, and contractual data-residency commitments directly with the provider before deployment.
Get Your Saudi Data Residency Strategy Right
Data residency is not simply a question of choosing a Saudi cloud region.
A strong data residency strategy starts with understanding which rules apply, what data you handle, where you store and process it, whether transfers occur, and which contractual and technical safeguards you need.
For organizations operating under Saudi privacy and cybersecurity requirements, bringing those questions together can make compliance reviews far more manageable.
Sahl helps organizations map data flows, document compliance requirements, track cross-border transfers, and keep privacy evidence organized for audit readiness.

